When Izhar Mujaddidi joined Coronis Health as CISO, his first security assessment put email at the top of the risk list. The existing stack was letting phishing and business email compromise (BEC) reach end-users. His team was small, and the tools that were supposed to help were generating more noise than signal.

Sixteen months after deploying Sublime, Coronis has seen a drastic change: zero BEC incidents, 90% reduction in time spent investigating email threats, and 90% fewer false positives.

In this webcast, Izhar joins Sublime to walk through the decision, the deployment, and what actually changed. They will cover: 

  • What the security assessment revealed, and why email rose to the top

  • Why the existing gateway left blind spots that better tuning couldn't close

  • How Sublime deployed in about a week, and what the team stopped having to do once ASA (Autonomous Security Analyst) took over investigation and response

  • What 16 months of results look like for a lean team that needed protection to run itself

If you're running a lean security team and wondering whether your email coverage is keeping pace with how attacks are evolving, this is for you.

Attendees are eligible to receive 1 CPE credit.

Generously supported by:
supported by logo
Speakers
speaker photo
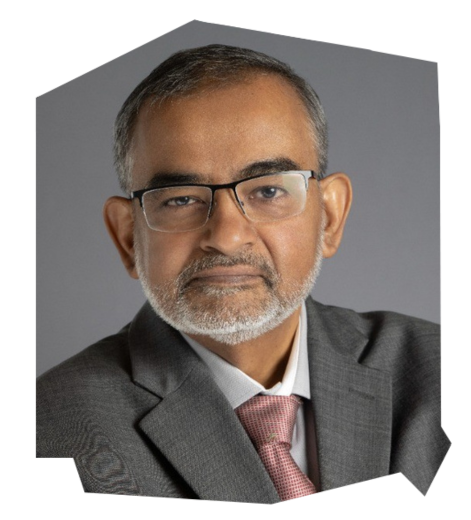
Izhar Mujaddidi
Global CISO, Coronis Health

As the Global Chief Information Security Officer at Coronis Health since December 2024, I lead the development and execution of the organization’s cybersecurity strategy, ensuring the protection of sensitive healthcare data and strict compliance with industry regulations. With a focus on robust security frameworks and risk management, my work supports the company’s business objectives while fostering a culture of security awareness across the enterprise.

With more than 20 years of experience in cybersecurity and information assurance, I specialize in implementing information security programs, governance risk compliance frameworks, and threat mitigation strategies. My leadership has been integral in safeguarding digital assets against evolving cyber threats, leveraging cutting-edge technologies and best practices to enhance organizational resilience and build trust with stakeholders.