Three weeks after attackers turned up the heat on roughly 700 French supermarkets, they've done it again—and this time the map is a lot bigger.
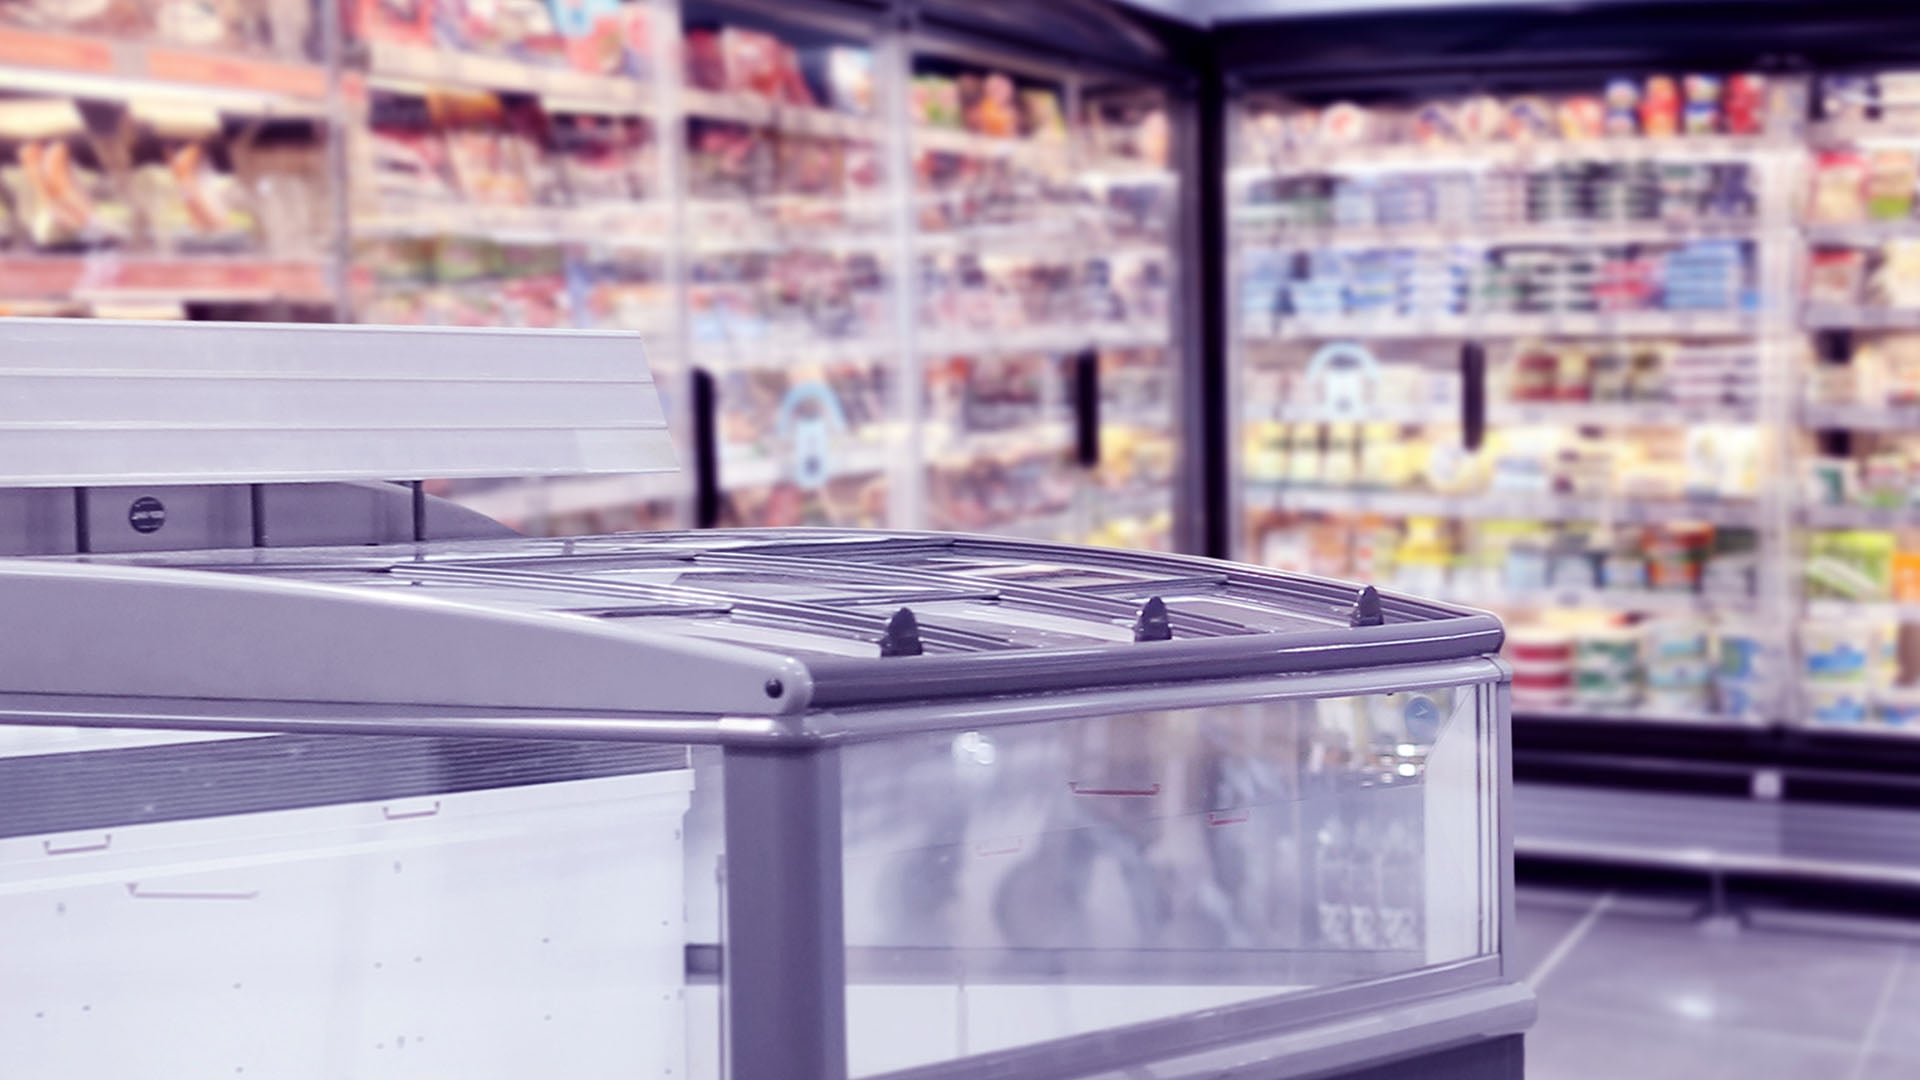
Overnight from Sunday to Monday, November 1-2, more than 100 stores in Belgium, Estonia, Ireland, Luxembourg, the Netherlands, and Sweden watched their fridges and freezers warm up. Some units were set as high as 50°C (122°F). Problems have since been reported in Finland, Italy, and Portugal, as well. Nobody has claimed responsibility.
And on the other side of the Atlantic, The New York Times reports that the Pentagon is now treating a string of mysterious freezer malfunctions that spoiled food at U.S. military bases in August as a suspected hack, according to four officials familiar with the matter.
No malware payload. No ransom note. No stolen data. Just a legitimate control function, abused at scale.
[RELATED: Danfoss Fridge Attack Wasn't a Visibility Failure]
What happened this time
The victims range from national chains to small neighborhood butcher shops. Belgium and Luxembourg took the heaviest hit, with around 40 Delhaize stores and 15 Carrefour supermarkets affected. In the Netherlands, refrigeration vendor Danfoss counted at least 17 smaller shops.
The retailers aren't hedging. "It's a cyberattack, there is no other reason," Carrefour Belgium spokesperson Mich Vergauwen told reporters, while adding that the impact on the chain was "very limited." Belgium's Centre for Cybersecurity (CCB) confirmed it was aware of the incident.
For individual stores, "limited" is relative. Belgian daily Het Laatste Nieuws reported that a single Delhaize location in Hoeilaart estimated its food losses at €100,000, not counting the cost of closing the store. In Sjöbo, Sweden, staff at an ICA Kvantum were photographed hauling spoiled product into dumpsters after freezer setpoints were pushed to 50°C.
The response is escalating at the policy level, too. Italy convened an emergency meeting on November 3, and the EU has said it will check supermarkets' readiness for cyberattacks.
Same playbook as France
The technique appears to be a direct replay of October. Stephan Moelans, CEO of Belgian refrigeration firm Sabcobel, which services Delhaize's systems, told the Belga news agency that the attackers forced the units' evaporators into defrost mode. That's exactly what happened in France.
That first wave struck overnight from October 11 to October 12. Refrigeration units at Intermarché, Carrefour, Coopérative U, and Monoprix stores were forced into defrost, spoiling food and reportedly sparking fires. CERT-FR, the incident response arm of France's national cybersecurity agency ANSSI, initially tied the compromises to Danfoss AK-SM and AK-SC series controllers. A day later, it widened the alert to include Copeland and Dixell XWEB systems. Danfoss said most of the hacked units were legacy products it no longer updates.
Investigators have not established whether the two waves are connected. But Moelans flagged the detail that should worry every OT security team: a software update alone won't fully close the hole. The affected equipment also needs to be physically modified.
The experts weigh in
Robert Costello, Chief Digital and Information Officer at Merlin Group, said he sees the incidents as one more proof point that control systems age far slower than the threats against them.
"These attacks continue to highlight the fragility of control systems," Costello said. "As the manufacturer highlights, sometimes software updates cannot completely resolve these issues, and the hardware in these systems must be replaced with more modern technologies. There is no simple answer; these systems are often deployed in environments where they operate for decades."
He also said he's skeptical that the usual architectural fix comes cheap: "While it is possible to employ zero-trust principles to provide some protection, this is not easy, and often requires a full rebuild of the environments to achieve results."
John Gallagher, Vice President at Viakoo, argues that October's disclosures effectively painted a target on the whole product category: "The Danfoss controller attacks put a big 'look here' sign for malicious hackers onto the refrigeration units; no surprise there are now follow-on copycat attacks that are expanding from the initial attacks."
Gallagher places the campaign within a broader shift toward operational ransomware, which holds operations hostage rather than data, and toward attacks with physical consequences. "These numbers are likely to keep rising as threat actors target systems with out-of-date firmware, simple passwords, or lacking certificates," he said. "Until automated cyber hygiene is the standard, like it is for IT systems, threat actors will focus on OT/IoT."
Louis Eichenbaum, Federal CTO at ColorTokens, zooms out to the national security picture. "Our adversaries are increasingly targeting the foundational elements of human life: water, electricity, and now our food supply," he said. "Even when these attacks fail to cause widespread disruption, they can create fear, undermine public confidence, and expose vulnerabilities in the infrastructure our communities depend on."
His sharpest warning is about what might come next. "My greatest concern is that we may be witnessing adversaries testing our defenses ahead of something much larger," Eichenbaum said. On the U.S. commissary incidents specifically, he notes that while no connection has been established, "successful attacks against military food supplies could directly affect logistics and operational readiness."
Who's behind it? Nobody knows yet
Attribution remains wide open, and the experts are careful not to overreach.
Gallagher points out that the cross-border coordination might suggest a nation-state, but notes that many other types of actors, from hacktivists and extortionists to hobbyists, would have both the means and the motivation.
Costello questions whether the answer even matters to those on the receiving end: "Attribution can be difficult, and to those affected it matters little if this is a nation-state or a criminal hacker gang. These attacks affect real people and place lives in danger."
That's the uncomfortable throughline here. Whoever is responsible didn't need zero-days or custom implants. As Eichenbaum puts it, "By manipulating legitimate control functions, such as forcing refrigeration systems into defrost mode, attackers can cause significant physical and economic damage without deploying sophisticated malware."
Why this matters beyond grocery
Refrigeration controllers rarely make the critical infrastructure shortlist. They don't carry the profile of a power grid or a water treatment plant. But they sit at the center of food safety, and they share every trait that makes OT hard to defend: decades-long service lives, vendor end-of-support, remote management bolted on for convenience, and owners who think of them as appliances rather than networked computers.
The same profile describes building management systems, HVAC, pharmacy cold storage, and hospital blood banks. If an attacker can spoil €100,000 of inventory in one store overnight with a mode change, the economics of this kind of attack are going to attract imitators. Gallagher's "copycat" observation suggests that's already happening.
What security teams should do now
The commentators converge on a short, practical list.
Find what's exposed. Inventory every refrigeration, HVAC, and building controller, and identify anything reachable from the internet. Eichenbaum's first priority is to "identify exposed assets, eliminate unnecessary internet access, and enforce strong authentication."
Close the front door. Gallagher recommends putting internet-facing consoles behind firewalls, turning off remote access controls, updating firmware, and rotating passwords immediately.
Retire what can't be fixed. "Systems that are end-of-life should be decommissioned immediately," Gallagher said. Given Moelans' point that software patches alone won't remediate the affected gear, budget for hardware replacement, not just maintenance windows.
Segment and contain. Remaining systems belong on segmented networks with tightly-controlled access. Eichenbaum adds microsegmentation, continuous monitoring, and tested recovery procedures to the list.
Plan to keep running. Eichenbaum frames the goal not as perfect prevention but as resilience: "Our measure of cybersecurity success must be whether we can contain an attack and keep the mission running."
Two waves in three weeks, nine-plus countries, a suspected link to U.S. military bases, and a vendor admitting much of the targeted fleet is beyond software repair. This is no longer a one-off incident; it's a stress test of how seriously we take the unglamorous machines that keep society running.
The attackers didn't steal anything; they just changed a setting. That should be the wake-up call for every organization still treating its OT estate as somebody else's problem.