A verified HBO Max Reddit account was hijacked and used to push 108 malicious ads over roughly 48 hours, redirecting users to fake app downloads that quietly infected their Windows and macOS devices with infostealer malware.
Security researchers at Hudson Rock and ADAMnetworks have tied the campaign to a broader operation they call PasteSwitch—named for its use of attacker-supplied commands that victims paste into their own systems, paired with a backend that switches between campaigns, platforms, and payloads depending on who clicks.
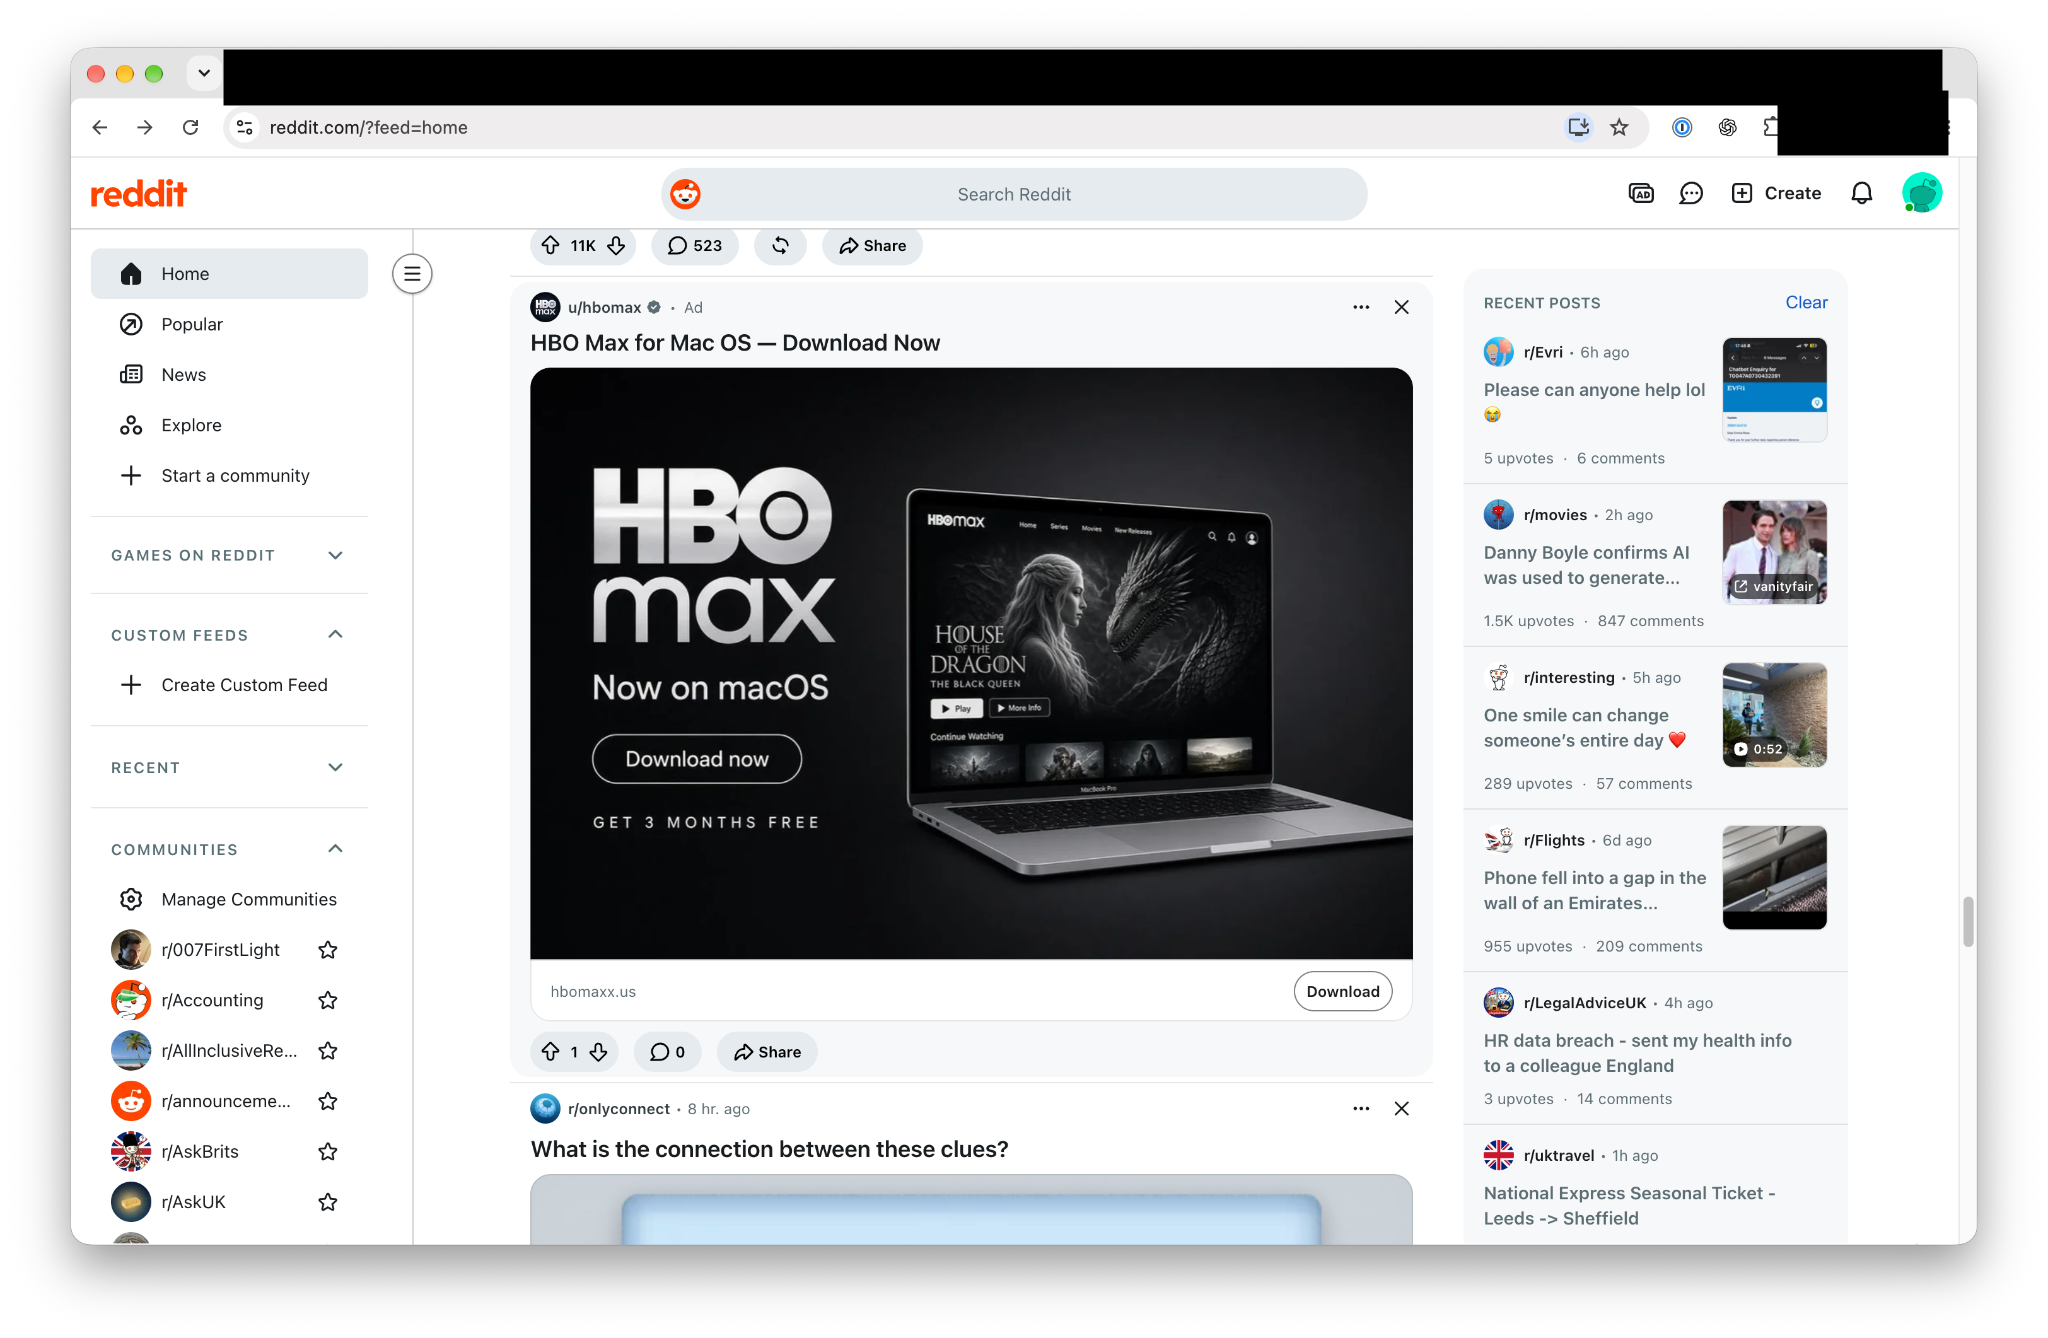 The malicious ad as it appeared in a Reddit feed, displaying the verified u/hbomax account, an "Ad" label, and the fake hbomaxx.us domain. (Source: u/Unhappy-Capital-1464/Reddit)
A user's catch, not a researcher's
The campaign came to light not through automated threat detection, but through a Reddit user flagging something that looked off. Posting to r/cybersecurity under the flair "Personal Support & Help!," u/Unhappy-Capital-1464 described spotting an ad authored by u/hbomax promoting a macOS HBO Max app they hadn't heard of. The account's verified status and history of posts in official HBO Max subreddits made it look legitimate at first glance.
Before assuming the account itself was fake, u/Unhappy-Capital-1464 checked for the more common explanation: a lookalike account using character substitution in the username. "I did consider some sort of character substitution in the username but clicking it took me to the profile," they wrote—ruling out a spoofed handle and pointing instead to a genuine account takeover.
The ad led to hbomaxx[.]us, described as looking "somewhat legitimate, and has a join button/download."
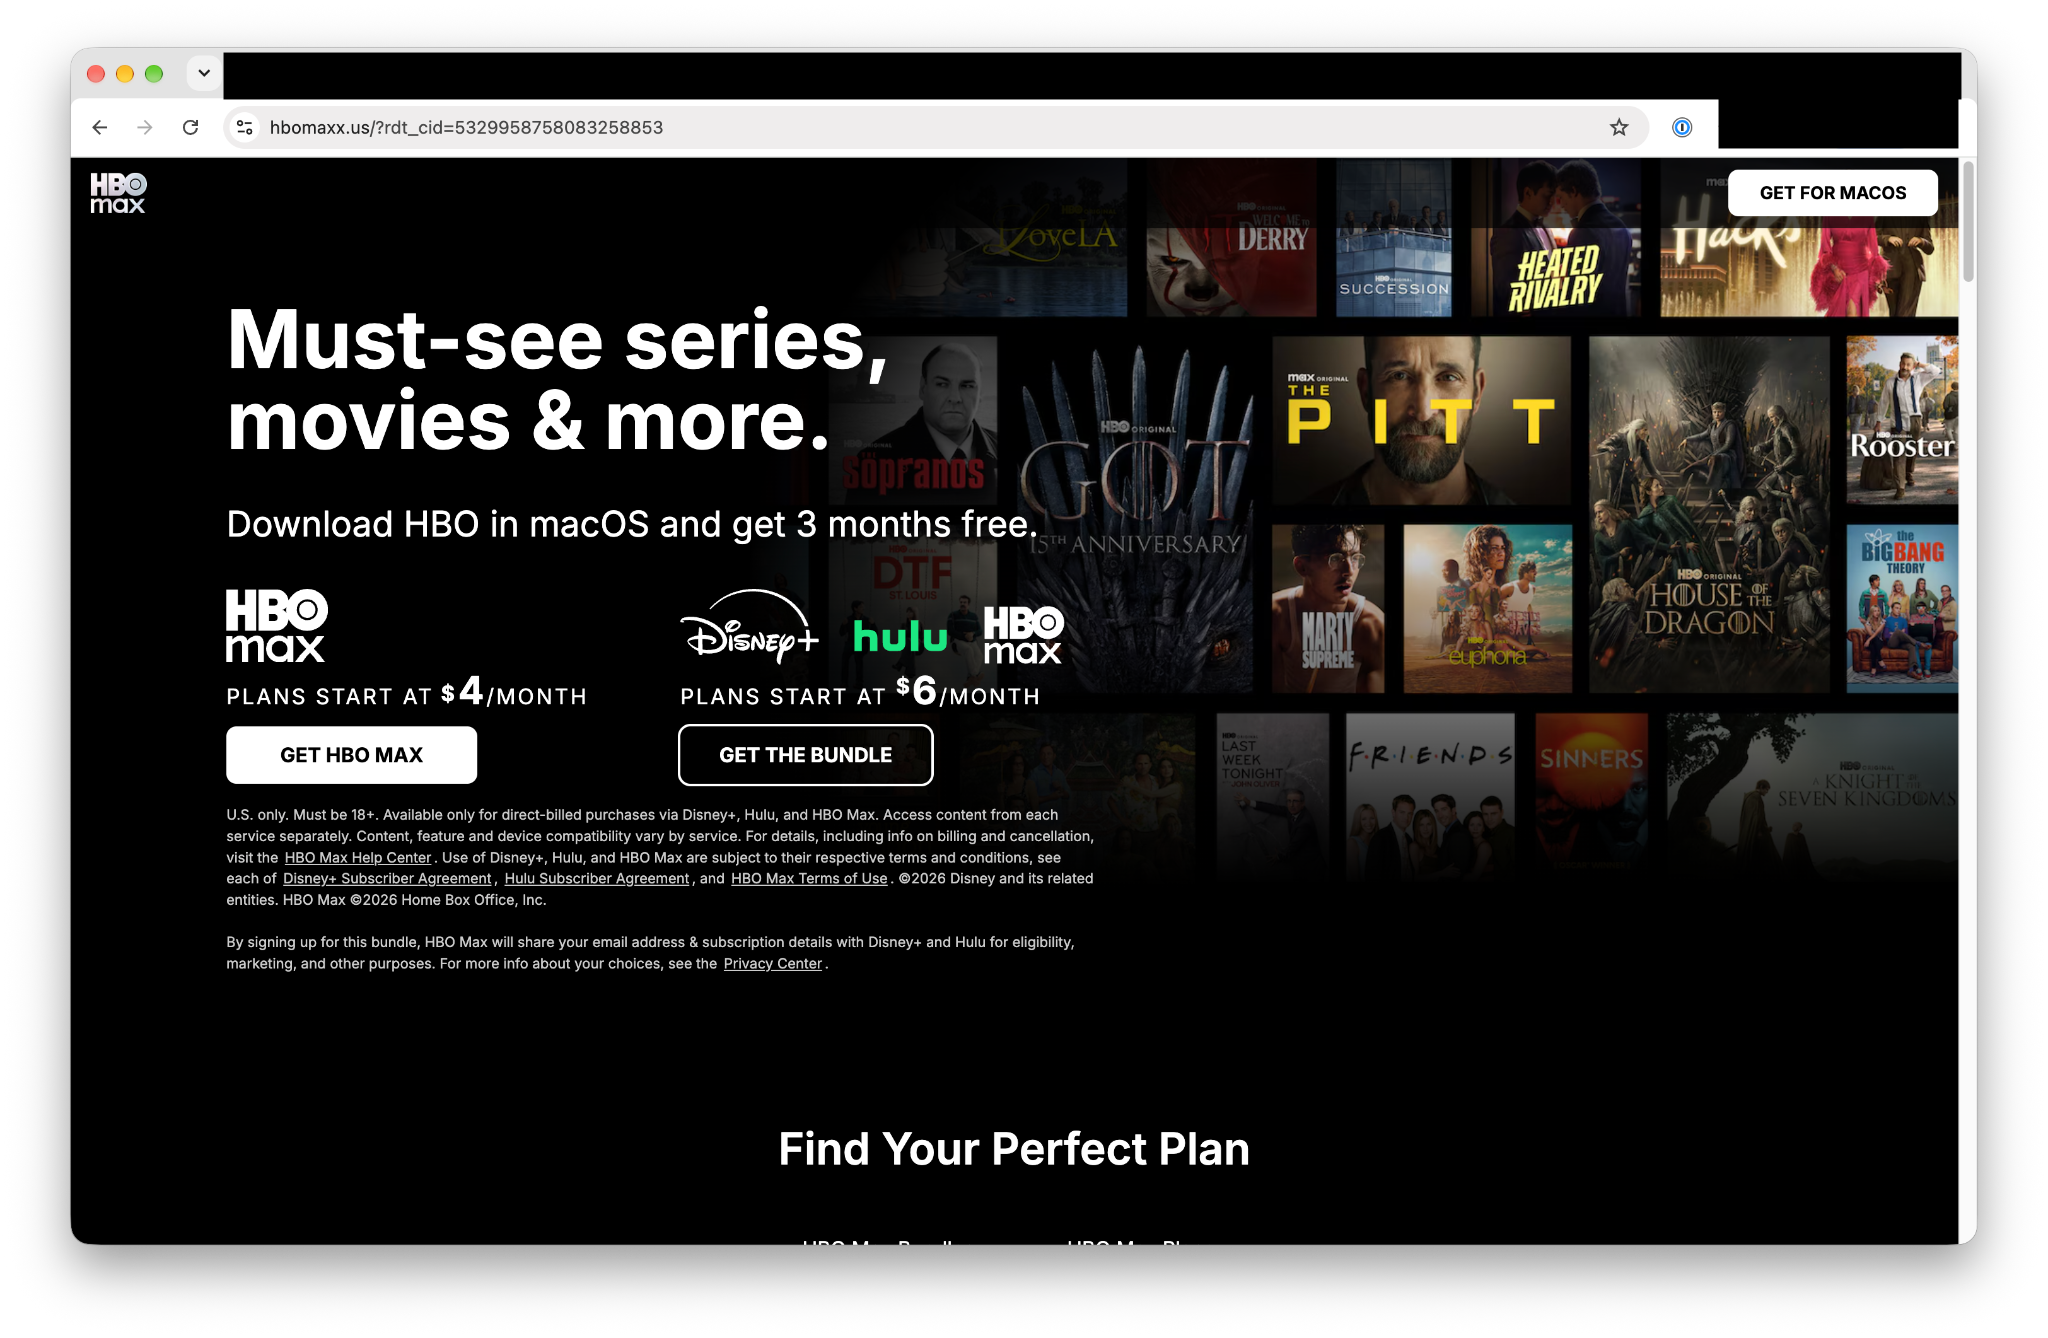 The fake hbomaxx.us landing page, styled to closely match HBO Max's real branding, pricing, and legal disclaimers. (Source: u/Unhappy-Capital-1464/Reddit)
Clicking through triggered what the poster recognized as "the classic infostealer/clickfix paste this command to download," and rather than run it, they tested the payload in a sandbox, inspecting its behavior without executing it on a live system. They reported the account directly to both Reddit and HBO.
Inside the ClickFix chain
The technique at work is ClickFix, a social engineering method that disguises a malicious command as a routine fix—a CAPTCHA check, an app install, an error resolution—and has the victim copy and paste it into Terminal, Run, or PowerShell themselves. Because the user executes the payload manually using legitimate system tools, ClickFix routinely slips past browser and endpoint protections built to catch file-based malware downloads.
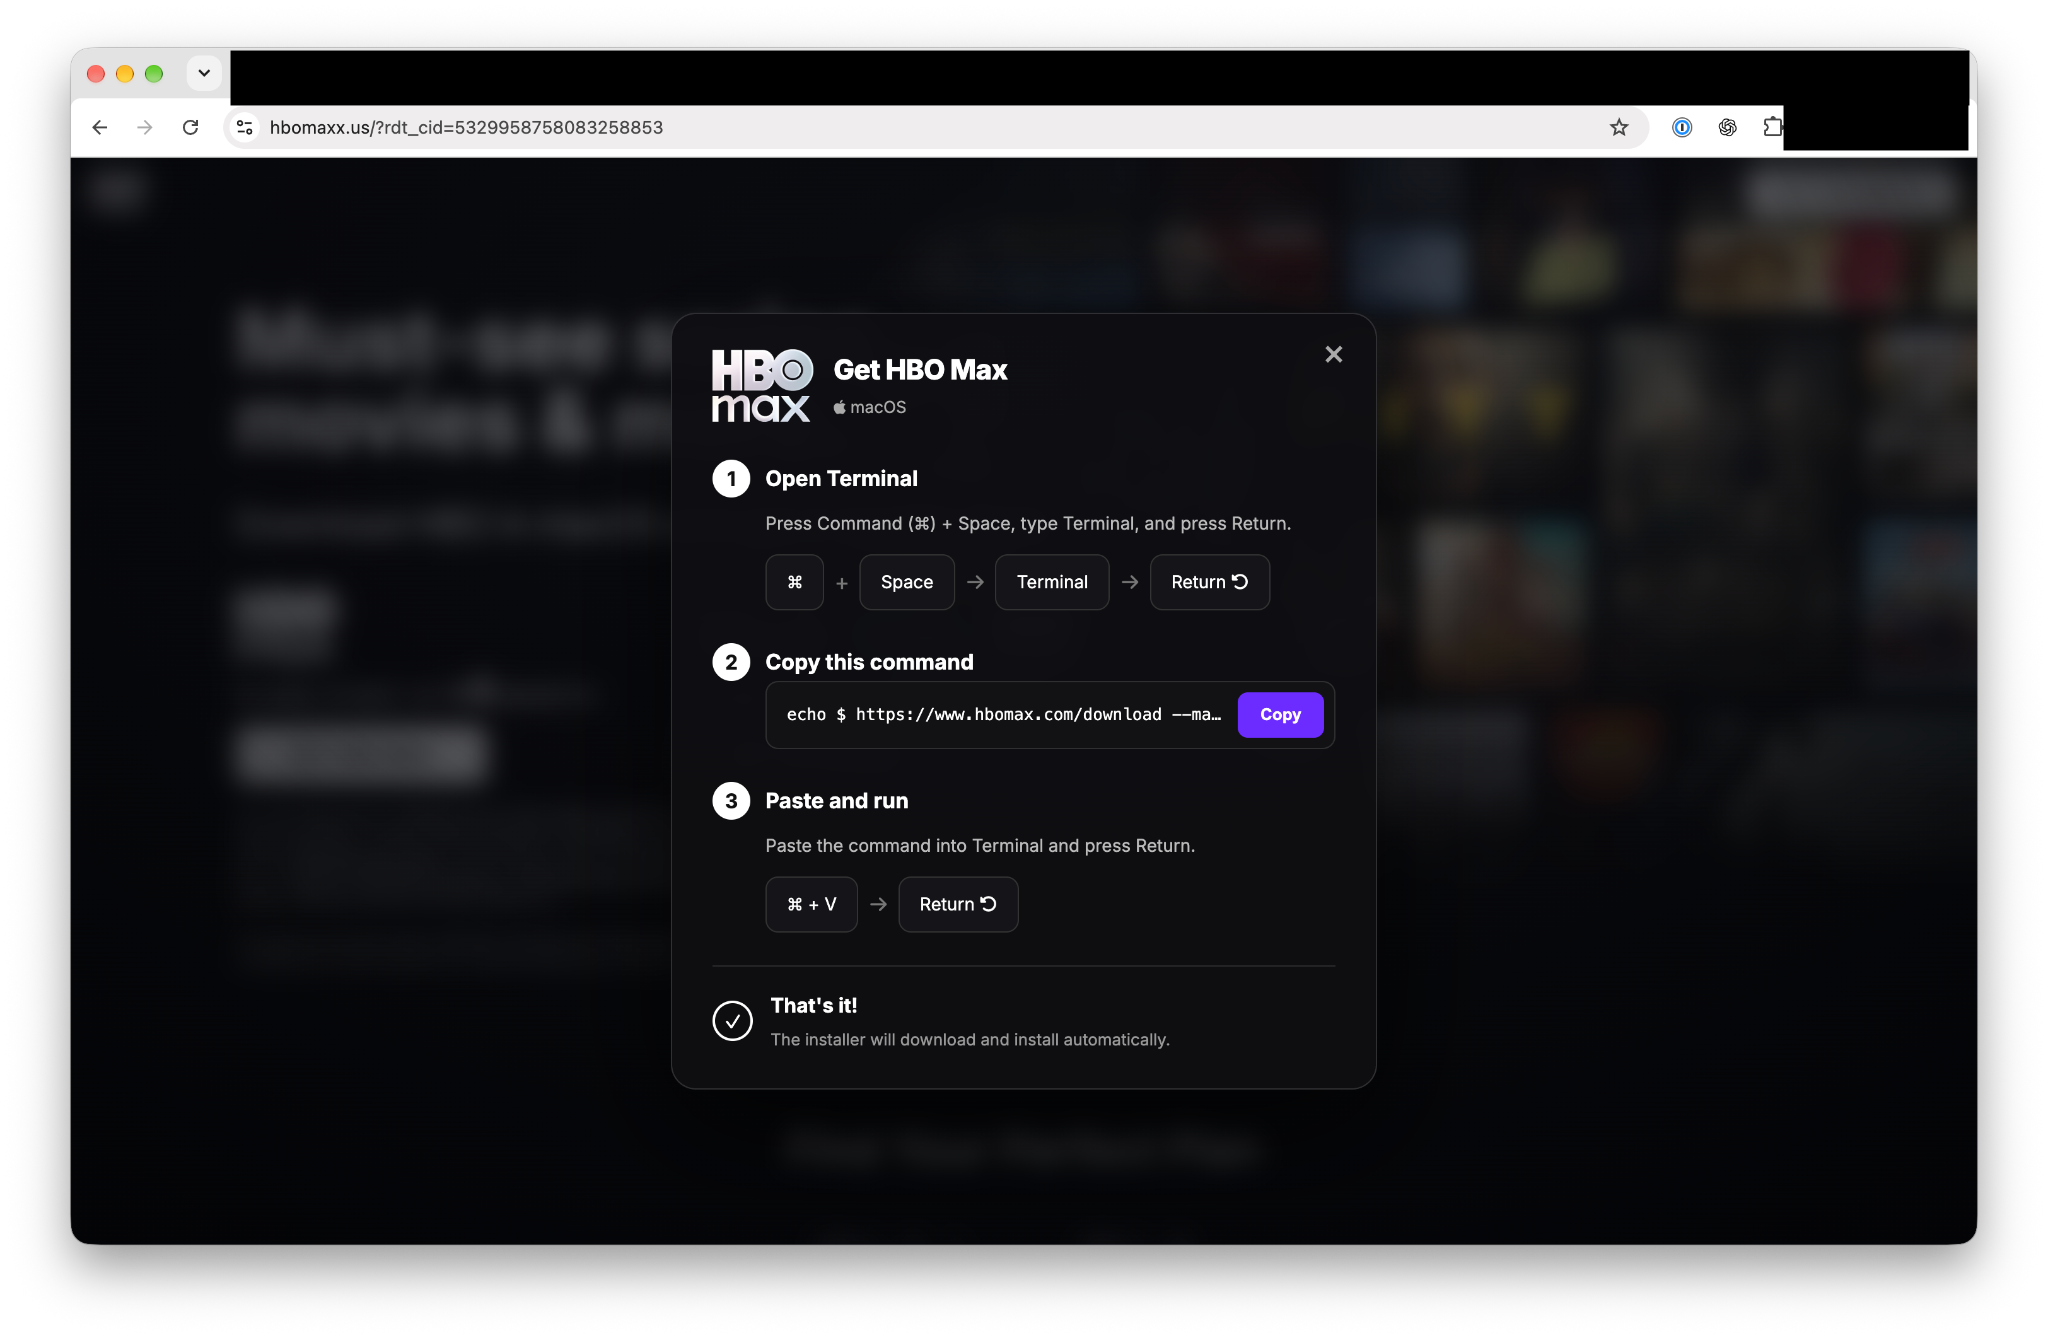 The "Get HBO Max" pop-up walks victims through opening Terminal and pasting a command, a hallmark of the ClickFix technique. (Source: u/Unhappy-Capital-1464/Reddit)
On macOS, one observed command was Base64-encoded to obscure its function; decoded, it pulled a payload from ember-bridge[.]com—infrastructure Hudson Rock has linked to PasteSwitch activity throughout September. The resulting malware included MacSync, which harvests browser credentials, Firefox profiles, Telegram data, Apple Notes, and macOS keychain passwords, and a tool researchers dubbed "AMOS helper"—a reference to the well-known Atomic macOS Stealer—that establishes persistence and can enroll infected machines with attacker-controlled infrastructure for further tasking.
On Windows, one attack chain used an MP3/HTA polyglot file to create a scheduled task, launch 32-bit PowerShell, disable the Antimalware Scan Interface, and generate victim-specific infrastructure keyed to the computer name and username. Later stages loaded Amatera Stealer directly into memory, skipping disk entirely. The campaign has also pushed clipboard-hijacking crypto malware—AnimateClipper and ZigClipper—along with fake Ledger, Trezor Suite, and Exodus wallet apps built to steal recovery phrases.
One brand among several
HBO Max wasn't the operation's only lure. Researchers identified 40 ads pointing to a second fake domain, hbomaxx[.]app; 36 promoting a fake AI/developer tool site, codex-craft[.]com; 15 for apple.clean-disk-guide[.]com; 11 for code-desktop[.]com; and six more for hbomax-macos[.]com—extending the campaign's reach well beyond streaming subscribers to developers and anyone searching for AI tools or system utilities.
Response and open questions
After the ads were reported, a Reddit admin paused them and escalated the incident to Reddit's Security and Safety teams. It remains unclear how the u/hbomax account was compromised, or whether other HBO or Warner Bros. Discovery accounts or systems were affected. HBO and Warner Bros. Discovery have not responded to requests for comment as of this publication.
Why it matters for practitioners
The incident reminds us that brand trust itself is an attack surface. Verified social accounts—the very thing meant to signal legitimacy to users—become high-value targets precisely because of the trust they carry, and a single compromised account can be repurposed to run a malvertising operation at scale before anyone notices.
Organizations that maintain official social presences should treat those accounts with the same access controls, monitoring, and incident-response readiness as any other privileged credential, and should have a process in place for the scenario this case illustrates: a user reporting something suspicious before the organization catches it.
[RELATED: GTA VI's Leak Crisis Shows Hype Itself Is Now an Attack Surface]