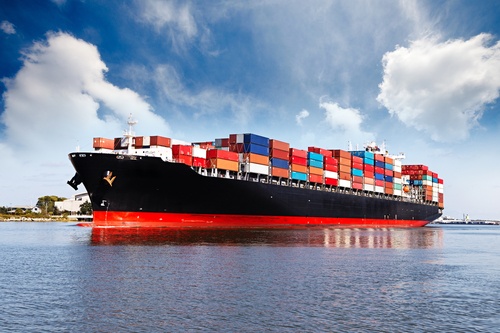
Shipping giant A.P. Moller - Maersk has confirmed that an attacker accessed and extracted data from a legacy system it inherited through a previous acquisition. The breach surfaced four years after the deal that brought the system in.
In a statement published November 11th, the company said its cybersecurity team began investigating immediately and secured the affected system. Maersk has not said what data were taken or how much. Its preliminary findings indicate that no sensitive information was disclosed. The company describes the incident as isolated to a local system and says it has found no sign of impact on other Maersk infrastructure, or on customer and partner systems that connect through APIs and electronic data interchange (EDI). Customers can keep booking and managing shipments as usual.
Two very different accounts
The attacker tells a different story. The WhiteArmor ransomware group listed Maersk on its data leak site over the weekend and demanded $5 million in Bitcoin, giving the company 30 days to pay, BleepingComputer reported. WhiteArmor claims to hold roughly 100GB from the former LF Logistics platform. It says the data include:
-
nearly 30,000 driver records
-
plaintext passwords and 33 SUPER_ADMIN accounts
-
signed delivery receipts
-
inventory records with purchase orders and Advance Shipping Notices
-
27,842 mobile device logs containing phone numbers, emails, and IMEI numbers
None of this has been independently verified, and ransomware groups routinely inflate their hauls to raise the pressure. Still, Maersk's "no sensitive data" finding sits uneasily next to a claimed inventory that includes credentials and administrator accounts, and that gap is worth watching as the investigation continues. If the platform really did store passwords in plaintext, it had gone a long time without modern security controls.
Maersk has told customers to treat any unexpected communications about the incident with caution, and to verify them through their usual Maersk contacts. That's a sensible precaution. Delivery records and contact data are exactly the material attackers use for follow-on phishing.
You bought it, you own it
The platform traces back to LF Logistics, the Hong Kong-based contract logistics firm Maersk acquired from Li & Fung in 2022 for $3.6 billion. The purchase added 223 warehouses and about 10,000 employees across Asia-Pacific, along with all the technology that came with them.
John Strand of Black Hills Information Security reacted with little patience for the "legacy" label in disclosures like this one. "You bought the company. As soon as the ink is dry, securing those systems is your responsibility," Strand said.
He draws a close parallel in the Oracle Health breach. In that incident, an attacker used compromised customer credentials to reach legacy Cerner servers that hadn't yet been migrated to Oracle Cloud. Oracle acquired Cerner in 2022, the same year Maersk closed on LF Logistics. A filing with the Texas Attorney General published in October put the nationwide toll at nearly 20 million people. "If something catastrophic happens, pointing to the previous owner isn't much of a defense," Strand said.
Why do these systems stay exposed so long? Seemant Sehgal, founder and CEO of BreachLock, points to what comes with the deal: separate credentials, a separate patch schedule, and connections into the parent network set up during integration and seldom reexamined. Ownership of those systems often becomes unclear after the deal closes. His advice is to find the problems before closing. "A penetration test during due diligence answers that before the deal closes," Sehgal said, "while there is still leverage to fix it."
The NotPetya contrast
Maersk knows what a worst case looks like. In 2017, NotPetya forced the company to reinstall about 45,000 PCs and 4,000 servers and to operate without IT for roughly 10 days, at a cost of around $300 million.
According to Damon Small, Xcape, Inc. board member, this week’s disclosure is evidence that those lessons stuck. In his assessment, the hard experience of 2017 matured Maersk's incident response. He also said that keeping the legacy system separated from core logistics networks and partner EDI connections is what kept cargo moving. "The $300 million lesson from 2017 paid off," Small said. "This time, the legacy server took the hit while the ships kept moving."
Two caveats apply. Maersk hasn't described its network architecture or how it contained the intrusion, so the role of segmentation is an informed reading, not a confirmed fact. And protecting operations is not the same as protecting the data. WhiteArmor's public demand shows the extortion phase is already underway.
Small's broader point is about how companies evaluate deals. He argues that cyber due diligence should get the same scrutiny as a financial audit, with inherited servers, databases, and applications identified and then promptly segregated or decommissioned.
Know what you own
The key questions are still open, according to Ridge Security's Darin Fredde: what the attackers accessed, how they got in, and whether the boundaries around the legacy environment actually held. "The lesson for organizations isn't simply to replace every legacy system," said Fredde, senior director and offensive security evangelist. "It's to know what you own, understand how inherited systems connect to the business, and continuously validate that the security controls protecting them work."
For security teams, that means four concrete steps:
-
Keep a current inventory of every system that came in through an acquisition.
-
Map what each of those systems can still reach.
-
Review integration-era credentials and connections on a regular schedule.
-
Set firm decommissioning dates instead of letting old platforms run indefinitely.
"An acquisition may close financially in a few months. The security obligations can last decades," Fredde said.